Google Workspace (formerly G Suite) SSO
SureMDM integrates with Google Workspace (formerly G Suite) through SAML 2.0 Single Sign-On (SSO). Users sign in to the SureMDM console with their Google Workspace credentials, so they don't need separate SureMDM credentials, and administrators manage access centrally in Google Workspace.
When a user signs in through Google Workspace SSO for the first time, SureMDM automatically creates the user in User Management with the permissions configured for the SSO setup under Dynamic Permission Assignment.
Prerequisites
- A Google Workspace account with super administrator access to the Google Admin console.
- A SureMDM account with permission to change Account Settings. Only Account Administrators can configure SSO permissions that grant Super User privileges.
- Your SureMDM server path.
- For condition-based rules in Dynamic Permission Assignment, the attributes used in the rules must be mapped in the Google Admin console.
The configuration is done in three steps:
- Create the custom SAML app in the Google Admin Console
- Configure SAML Single Sign-On in the SureMDM Console
- Update the Google Admin console with the SureMDM Assertion URL
Step 1: Create the custom SAML app in Google Admin console
Create the application
- Sign in to the Google Admin console (admin.google.com) with a super administrator account.
- Navigate to Apps > Web and mobile apps.
- Click Add app > Add custom SAML app.
- On the App details page, enter any friendly name for the application (for example, SureMDM SSO) and click Continue.
Copy the Google values and download the certificate
- On the Google Identity Provider details page, under Option 2, copy the following values. You will paste them into SureMDM in Step 2.
- SSO URL
- Entity ID
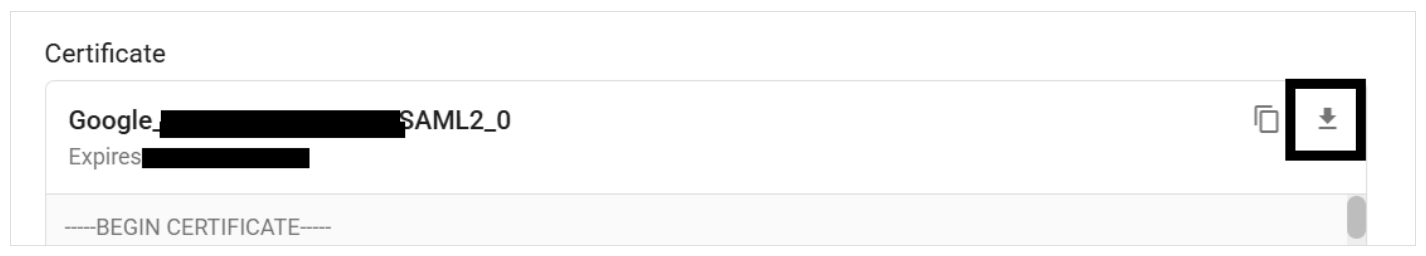
- Click Download certificate, then click Continue. Please refer to the Screenshot below:
Configure Service provider details
- On the Service provider details page, enter the following values:
| Field | Value |
|---|---|
| ACS URL | https://<SureMDM Server Path>/console/ssoconsumer/<Encrypted Account ID> |
| Entity ID | urn:42gears:suremdm:SAML2ServiceProvider |
| Name ID format | |
| Name ID | Basic Information > Primary email |
- Leave Start URL empty and Signed response unchecked.
- Click Continue.
In the ACS URL, <SureMDM Server Path> is the SureMDM console URL & <Encrypted Account ID> is the encrypted Account ID.
The Encrypted Account ID is generated by SureMDM only after the SAML Single Sign-On settings are saved (Step 2). Google Admin console requires an ACS URL before you can continue, so for now enter your SureMDM Account ID as a placeholder in place of the Encrypted Account ID. You will replace it with the actual URL in Step 3.
Configure Attribute mapping
- On the Attribute mapping page, you can either add attribute mappings now or leave this page empty. Mappings can also be added later from the app's SAML attribute mapping section (refer to Add attribute mapping in Google Admin console).
- Click Finish.
Turn on user access
After you create the app, the Google Admin console opens the app's details page. User access for a new custom SAML app is OFF for everyone by default. Only users for whom the app is turned on can sign in to SureMDM through Google Workspace. Other users receive error 403 app_not_configured_for_user from Google.
You can turn on the app for your whole organization, for specific organizational units, or for a set of users through an access group.
- On the app's details page, click User access. If you have navigated away, go to Apps > Web and mobile apps and open the app first.
- Choose who can use the app:
- Everyone in your organization: select ON for everyone.
- An organizational unit: select the organizational unit at the left, then set Service status to ON.
- A set of users across or within organizational units: select an access group.
- Click Save.
Changes can take up to 24 hours but typically happen more quickly. Users who sign in to SureMDM through Google Workspace must use the same email address they use to sign in to Google Workspace.
For more information, see Google's documentation on setting up your own custom SAML app.
Verification: The app is saved in the Google Admin console, you have copied the SSO URL and Entity ID, you have downloaded the certificate, and user access is turned on.
Step 2: Configure SAML Single Sign-On in the SureMDM console
- Log in to the SureMDM Web Console.
- Navigate to Settings (gear icon at the top right) > Account Settings > Enterprise Integrations > SAML Single Sign-On.
- Click Add.
- In Select Identity Provider (IdP), select Google G Suite.
- On the SSO Configuration tab, configure the following settings:
| Setting | Description |
|---|---|
| Service Identifier | Paste the Entity ID copied from the Google Admin console. Example: https://accounts.google.com/o/saml2?idpid=<IdP ID> |
| Sign On Service URL | Paste the SSO URL copied from the Google Admin console. Example: https://accounts.google.com/o/saml2/idp?idpid=<IdP ID> |
| Logout Service URL | Paste the SSO URL copied from Google Admin console. This is generally the same as the Sign On Service URL. |
| SSO Service Provider Name | Enter urn:42gears:suremdm:SAML2ServiceProvider |
| Display Name | (Optional) A name that identifies this configuration in the SAML Single Sign-On list. |
Click Upload Certificate, select the certificate downloaded from Google Admin console, leave the password field empty, and click OK.
Open the Dynamic Permission Assignment tab and configure the Default Permission: select the Roles, Device Group Set, Jobs/Profiles Folder Set, and Remote File Manager Access Control to assign to users who sign in through Google Workspace. To assign permissions based on SAML attributes, see Dynamic Permission Assignment.
ImportantThe Default Permission applies to every user who has access to the app in Google Workspace and does not match a Dynamic Permission Assignment rule. If the app is turned on for everyone in your organization, any Google Workspace user can sign in to SureMDM with these permissions.
- Keep the Default Permission at the lowest level of access.
- Enable Deny Access to allow only users who match a configured rule to sign in. Users who do not match any rule are blocked instead of receiving the default permissions.
Click Save.
On the SAML Single Sign-On screen, locate the saved configuration and copy the full URL from the Assertion URL column. It contains your Encrypted Account ID and has this format:
https://<SureMDM Server Path>/console/ssoconsumer/<Encrypted Account ID>
Use Modify to edit a saved configuration, and Enable/Disable to turn SSO on or off without deleting the configuration.
Step 3: Update Google Admin console with the Assertion URL
- In the Google Admin console, navigate to Apps > Web and mobile apps and open the app created in Step 1.
- Click Service provider details to expand it.
- In the ACS URL, replace the placeholder with the exact Assertion URL copied from SureMDM.
- Click Save.
Sign in to SureMDM using Google Workspace SSO
- Open the SureMDM login page and click Sign In using SSO.
- Click the Google icon and sign in with your Google Workspace credentials.
Alternatively, use the URL shown in the Login URLs column of the SAML Single Sign-On screen, in this format:
https://<SureMDM Server Path>/console/ssologin/<Encrypted Account ID>
Add attribute mapping in Google Admin console
Attribute mappings specify which user attributes Google includes in the SAML assertion it sends to SureMDM during sign-in. They are required only for condition-based rules in Dynamic Permission Assignment.
Please refer to Set up your own custom SAML app for how to map user attributes and group membership.
The steps are the same for an existing app and a new app.
- In the Google Admin console, navigate to Apps > Web and mobile apps and open the SureMDM app.
- Click SAML attribute mapping.
- Add the required mappings and click Save.
Dynamic Permission Assignment
Dynamic Permission Assignment assigns different SureMDM permissions to users based on any attribute Google sends in the SAML assertion, for example, the user's group, name, or employee ID. When a user signs in, SureMDM compares the attribute values against your rules and assigns the permissions of the matching rule.
How SureMDM evaluates a sign-in
| Situation | Result |
|---|---|
| An attribute matches a rule (Attribute + Condition + Value) | The user is allowed to sign in and is assigned the Role, Device Group Set, Jobs/Profiles Folder Set and Remote File Manager Access Control configured for that rule. |
| No rule matches | The user gets the Default Permission. |
| No rule matches, and Deny Access is enabled in Default Permission | The user is not allowed to sign in to SureMDM. |
Default Permission is the fallback entry. Its Attribute, Condition, and Value fields are disabled because it applies to every user who does not match another rule. Set it to the lowest level of access you are comfortable giving any Google Workspace user who has access to the app.
Deny Access is available only in Default Permission. Enable it when only users who match a rule should be able to sign in (for example, only members of a SureMDM-Admins group). Users who do not match any rule are then denied access instead of receiving default permissions.
Configure Google Admin console
The attribute you want to use in a SureMDM rule must be sent as an App attribute in the SAML assertion.
Attributes sent by default
A new custom SAML app in Google Admin console sends only the following by default:
| Attribute | Value |
|---|---|
| Name ID | Primary email |
Any other attribute, such as first name, last name, employee ID, or group membership, must be added as an attribute mapping before it can be used in SureMDM. See Add attribute mapping in Google Admin console.
The Attribute name entered in SureMDM must exactly match the App attribute name in the Google Admin console. Attributes such as Employee ID are sent only if they are populated on the user's profile in Google Workspace. For group membership, Google sends only the selected groups that the user is a member of (a maximum of 75 groups can be selected).
Sample attributes
App attribute names are examples; you can use any name, as long as the same name is entered in SureMDM.
| Use case | Example App attribute | Example Value in SureMDM |
|---|---|---|
| Group | Groups | Dev (group name) |
| First name | firstname | John |
| Last name | lastname | Smith |
| Employee ID | employeeId | EMP1024 |
Configure SureMDM
Navigate to Settings (gear icon) > Account Settings > Enterprise Integrations > SAML Single Sign-On.
Select the Google G Suite configuration and click Modify (or click Add and complete Step 2 for a new configuration).
Open the Dynamic Permission Assignment tab.
Configure the Default Permission, and enable Deny Access if users who do not match any rule should be blocked.
Click Add to create a rule and configure the following settings:
| Setting | Description |
|---|---|
| Attribute | Name of any App attribute present in the SAML assertion, for example Groups, lastname or employeeId. |
| Condition | How SureMDM matches the attribute value with the rule value: Contains: the attribute value includes the specified value. Equals: the attribute value exactly matches the specified value. In: the attribute value matches one of the specified values. |
| Value | The value to match for the attribute, for example, a group name or an employee ID. |
| Roles | Role to assign when the rule matches. See Configure Permissions for Role-Based Admin. |
| Device Group Set | Device group set to assign when the rule matches. See Configure Permissions for Device Group Set Based Admin. |
| Jobs/Profiles Folder Set | Jobs/profiles folder set to assign when the rule matches. See Configure Permissions for Job Folder Set Based Admin. |
| Remote File Manager Access Control | Remote File Manager access control to assign when the rule matches. See Configure Permissions for Remote File Manager Based Admin. |
- Click Save.
For more information on SAML apps in Google Workspace, see Google's documentation: Set up your own custom SAML app.
The third-party configuration steps in this article are based on Google's documentation available at the time of publication and may change. Always refer to the official Google documentation for the latest instructions.